
SSO with Okta
SSO with Okta
Section titled “SSO with Okta”This guide covers the configuration of Single Sign-On (SSO) authentication for rConfig V8 using Okta. The process involves creating an OpenID Connect (OIDC) application in Okta and configuring rConfig with the necessary credentials.
When to Use This Page
Section titled “When to Use This Page”Follow this guide when your organization uses Okta for identity management and you want rConfig users to log in with their existing Okta credentials instead of a local rConfig password.
Prerequisites
Section titled “Prerequisites”- Administrator access to Okta Admin Console
- Administrator access to rConfig V8
- rConfig server accessible via HTTPS with valid domain name
Configure Okta
Section titled “Configure Okta”Step 1: Create App Integration
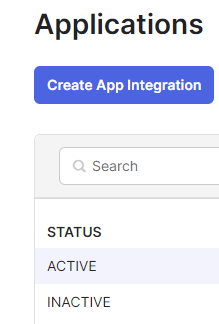
Section titled “Step 1: Create App Integration”In the Okta Admin Console, navigate to Applications > Create App Integration.
Step 2: Select Integration Type
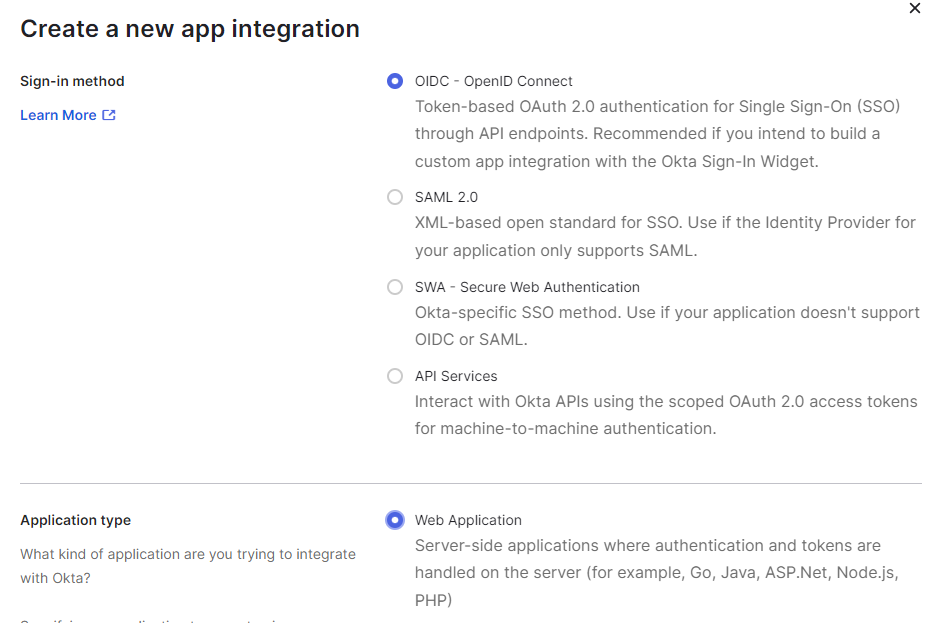
Section titled “Step 2: Select Integration Type”When the wizard launches:
- Select OIDC - OpenID Connect as the sign-in method
- Select Web Application as the application type
- Click Next
Step 3: Configure Application Settings
Section titled “Step 3: Configure Application Settings”Fill out the application configuration form:
General Settings:
- App integration name: Choose a descriptive name (e.g., “rConfig V8”)
Grant type:
- Check Authorization Code
- Check Refresh Token
Sign-in redirect URIs:
https://your-rconfig-domain.com/auth/callback/oktaSign-out redirect URIs:
https://your-rconfig-domain.comAssignments:
- Choose Controlled access based on your organization’s requirements
- Select the appropriate user or group assignments
Click Save to create the application.
Step 4: Assign Users or Groups
Section titled “Step 4: Assign Users or Groups”After the application is created:
- Navigate to the Assignments tab
- Click Assign and select Assign to People or Assign to Groups
- Assign the users or groups that should have access to rConfig via SSO
- Click Done
Step 5: Retrieve Configuration Details
Section titled “Step 5: Retrieve Configuration Details”From the application General tab, copy the following values:
- Client ID
- Client secret (click Show to reveal)
Step 6: Get Okta Base URL
Section titled “Step 6: Get Okta Base URL”- Navigate to Security > API > Authorization Servers
- Locate the Issuer URI for the default authorization server
- Copy only the hostname portion (e.g.,
https://your-domain.okta.com) - Do not include
/oauth2/defaultin the base URL
Configure rConfig V8
Section titled “Configure rConfig V8”Step 1: Edit Environment Configuration
Section titled “Step 1: Edit Environment Configuration”Open the rConfig .env file:
vim /var/www/html/rconfig8/current/.envStep 2: Add Okta SSO Configuration
Section titled “Step 2: Add Okta SSO Configuration”Add or update the following lines with your Okta application values:
OKTA_BASE_URL=https://your-domain.okta.comOKTA_CLIENT_ID=your_client_idOKTA_CLIENT_SECRET=your_client_secretOKTA_REDIRECT_URI=https://your-rconfig-domain.com/auth/callback/oktaConfiguration Parameters:
OKTA_BASE_URL: Your Okta domain (hostname only, without/oauth2/default)OKTA_CLIENT_ID: Client ID from Okta application settingsOKTA_CLIENT_SECRET: Client secret from Okta application settingsOKTA_REDIRECT_URI: Must match the sign-in redirect URI configured in Okta
Step 3: Clear Application Cache
Section titled “Step 3: Clear Application Cache”Save the file and clear the rConfig cache:
php /var/www/html/rconfig8/current/artisan rconfig:clear-allVerify Configuration
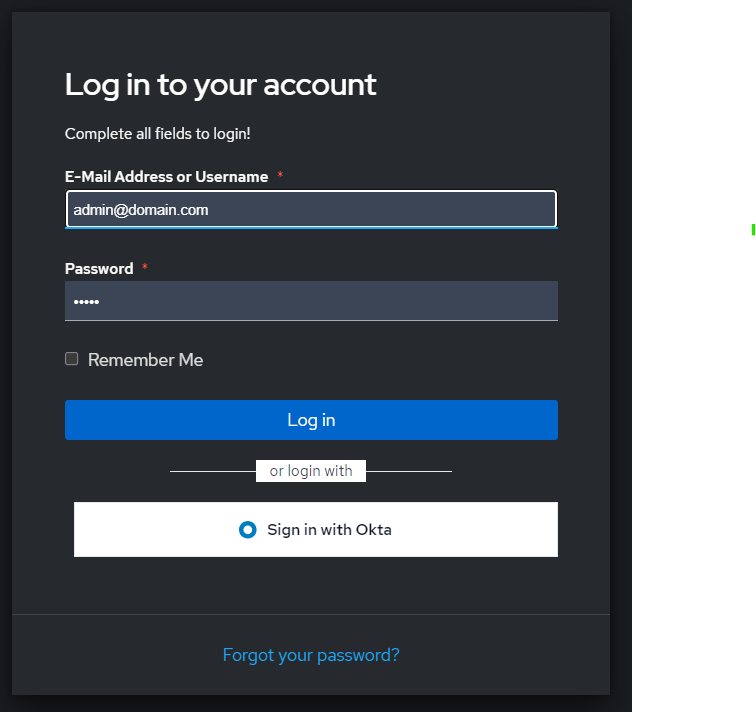
Section titled “Verify Configuration”After configuration, the rConfig login page will display a Sign in with Okta button.
User Approval Process
Section titled “User Approval Process”When users attempt to sign in via SSO for the first time:
- User authenticates successfully with Okta
- User account is created in rConfig with SSO access disabled
- User sees an error message indicating approval is required
Administrator must:
- Log in to rConfig as an administrator
- Navigate to Users section
- Locate the new SSO user
- Enable SSO access for the user
- Assign appropriate role and permissions
After approval, the user can successfully authenticate and access rConfig.
Common Gotchas
Section titled “Common Gotchas”Troubleshooting
Section titled “Troubleshooting”SSO button not appearing
Section titled “SSO button not appearing”- Verify all environment variables are correctly set
- Ensure cache has been cleared:
php artisan rconfig:clear-all - Check Apache error logs for configuration issues
Authentication fails
Section titled “Authentication fails”- Verify redirect URI matches exactly between Okta and rConfig
- Confirm Okta base URL does not include
/oauth2/default - Check that the application is assigned to the user in Okta
- Ensure client secret has not been regenerated in Okta
“Access denied” error from Okta
Section titled ““Access denied” error from Okta”- Verify user or group is assigned to the application in Okta
- Check that the application is active (not disabled)
- Confirm authorization server is active
Invalid redirect URI error
Section titled “Invalid redirect URI error”- Verify sign-in redirect URI in Okta matches exactly with
OKTA_REDIRECT_URIin rConfig - Ensure there are no trailing slashes or typos
- Check that HTTPS is used (not HTTP)
Users cannot access after SSO login
Section titled “Users cannot access after SSO login”- Verify administrator has enabled SSO access in Users section
- Confirm user has been assigned an appropriate role
- Check user account status is active
Related Documentation
Section titled “Related Documentation”- SSO Overview - Understanding SSO in rConfig V8
- User Management - Managing user accounts and approvals
- Roles and Permissions - Configuring user roles and permissions